

✒️ Foreword
Some people collect stamps. Others collect coins. Paul Erdős collected mathematical problems, friendships, and co-authors.
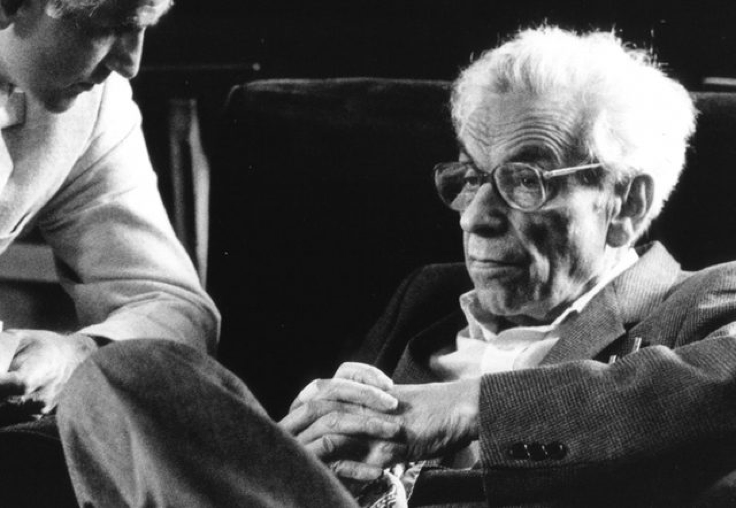
The legendary Hungarian mathematician (1913–1996) spent much of his life traveling from one university to another, living out of a suitcase and working with whoever was willing to tackle a difficult problem. He had no permanent home for much of his adult life, but he had something arguably more interesting: a global network of brilliant minds.
Over his lifetime, Erdős published more than 1,500 mathematical papers with over 500 collaborators. His network became so extensive that mathematicians invented the Erdős number to measure how closely connected they were to him through scientific collaboration.
But the fascinating part isn't the number of papers he published. It's the philosophy behind them.
Erdős understood that knowledge grows faster when people work together. A problem that seems impossible to one person might become solvable when approached from another perspective. And the more people contribute, challenge assumptions, and build upon each other's discoveries, the further everyone advances.
I think about this whenever I look at the work being done by the OWASP community.
Thousands of security researchers, developers, governance professionals, and volunteers contribute their expertise to identify vulnerabilities, develop standards, and create practical guidance. Much of this work is freely available, continuously improved, and built upon by people who may never meet their fellow contributors.
And that's what makes OWASP remarkable. It's not simply a collection of security frameworks. It's a living demonstration of what happens when people choose collaboration over working in isolation.
This edition of AIGL brings together some of that collective work: from the latest LLM and agentic AI security risks to practical guidance on securing AI systems, assessing vulnerabilities, and building effective governance.
Erdős spent his life connecting people through mathematics. Decades later, communities like OWASP are doing something remarkably similar through security.
Different problems. Different generations. The same fundamental idea: the most important work is rarely accomplished alone.
— Kuba
Curator, AIGL 📚
☀️Spotlight Resources
OWASP Top 10 for LLM Applications 2026
What it is:
Published in August 2026, this is the latest edition of OWASP's flagship framework identifying the most critical security risks affecting applications built with large language models. Replacing the 2025 edition, it incorporates updated risk rankings, expanded threat coverage, attack scenarios, and mitigation guidance informed by real-world incidents and community research.
Why it's worth reading:
The framework provides a practical starting point for LLM application threat modeling, security assessments, and risk management. Its mappings to NIST, MITRE ATLAS, CWE, and OWASP's agentic security guidance help organizations integrate AI-specific vulnerabilities into existing cybersecurity programs. Security teams should use the 2026 edition when updating their risk registers, development requirements, and testing procedures rather than continuing to rely exclusively on the previous version.
OWASP Top 10 for Agentic Applications 2026
What it is:
Released in December 2025, this framework identifies ten critical security risks associated with autonomous AI agents and systems capable of planning, executing actions, interacting with tools, and coordinating across workflows. Developed through contributions from more than 100 security experts and practitioners, it addresses threats that extend beyond conventional LLM vulnerabilities.
Why it's worth reading:
The framework focuses on risks created by granting AI systems operational autonomy. These include agent goal hijacking, tool misuse, identity and privilege abuse, memory poisoning, insecure inter-agent communication, and cascading failures. It provides a useful foundation for assessing agentic applications before deployment, defining appropriate security boundaries, and identifying where existing application security controls need to be extended. Particularly relevant for organizations adopting autonomous workflows, multi-agent architectures, and AI systems with access to enterprise tools.
OWASP GenAI Data Security Risks & Mitigations 2026
What it is:
Published in March 2026, this guide examines the data security challenges introduced by generative AI applications. It addresses the AI data lifecycle, including training and fine-tuning datasets, user prompts, model inputs, generated outputs, and the mechanisms through which sensitive information may be exposed or manipulated.
Why it's worth reading:
The publication offers a data-centric perspective on AI security that complements the broader OWASP Top 10 frameworks. It emphasizes integrating security testing, validation, and continuous monitoring throughout AI development and deployment.
For organizations handling confidential business information, personal data, or proprietary datasets, it provides a useful basis for reviewing AI data flows, establishing protective controls, and identifying weaknesses in existing data security programs. It is particularly relevant for security, privacy, and data governance teams working together on enterprise AI adoption.
OWASP Agentic Skills Top 10: Security Risks and Mitigations for Agentic Skill Ecosystems
What it is:
A security framework focused on reusable AI agent skills: packages containing instructions, executable code, configuration, and supporting resources that agents can discover and execute.
It examines the security implications of introducing external or dynamically loaded capabilities into autonomous AI environments.
Why it's worth reading:
Agent skills create an additional attack surface that is not fully addressed by conventional application security or even the broader Agentic Top 10.
Because skills may inherit an agent's permissions, malicious instructions or compromised dependencies can influence behavior and trigger unauthorized actions.
The framework is particularly useful for organizations adopting skill-based agent architectures, developing internal skill repositories, or assessing third-party agent capabilities. It provides a foundation for establishing security requirements around skill provenance, permissions, execution boundaries, and supply chain integrity.
OWASP Top 10 for LLM Applications 2025
What it is:
The previous edition of OWASP's flagship LLM application security framework, published in November 2024 and designated as the 2025 version.
It identifies ten major vulnerabilities in LLM-enabled applications, including prompt injection, sensitive information disclosure, supply chain risks, data poisoning, excessive agency, and weaknesses in retrieval systems.
Why it's worth reading:
Although superseded by the 2026 edition, the framework remains useful for understanding how OWASP's approach to LLM security has evolved.
Comparing the editions reveals changes in vulnerability prioritization, threat definitions, and the increasing importance of agentic capabilities.
It is particularly relevant for organizations that previously incorporated the 2025 categories into security policies, risk registers, or assessment methodologies and now need to update those references.
A Practical Guide for Secure MCP Server Development
What it is:
Published in February 2026, this technical guide addresses security considerations when developing Model Context Protocol servers connecting AI applications to external tools, APIs, and enterprise data sources. It examines the security implications of delegated permissions, dynamic tool access, and chained operations.
Why it's worth reading:
MCP infrastructure introduces security challenges that traditional API security practices do not fully address. The guide translates these challenges into concrete engineering recommendations covering authentication, authorization, input validation, session isolation, secure architecture, and deployment hardening.
Its particular strength is its focus on security at the integration layer, where AI applications gain the ability to interact with external systems. Development teams can use it to establish MCP security requirements, review implementation choices, and reduce vulnerabilities before exposing sensitive enterprise systems to AI agents.
CheatSheet: Securely Using Third-Party MCP Servers 1.0
What it is:
Released in November 2025, this guide addresses the security risks of connecting AI systems to MCP servers developed or operated by third parties. It examines threats including tool poisoning, prompt injection, memory poisoning, and interference between connected tools.
Why it's worth reading:
Unlike guidance focused on building secure MCP infrastructure, this resource addresses the risks of consuming external MCP services.
It provides recommendations for authentication, authorization, sandboxing, secure server discovery, least-privilege access, and human oversight. Organizations can use these recommendations when establishing approval processes for third-party MCP integrations, assessing external providers, and defining restrictions on the tools available to AI agents.
Particularly useful for organizations introducing MCP-based integrations into enterprise environments without developing every component internally.
Securing Agentic Applications Guide
What it is:
An 81-page technical guide published by the OWASP Agentic Security Initiative in July 2025. It provides recommendations for designing, developing, deploying, testing, and operating secure agentic AI applications.
The publication translates agentic AI threats into practical security architecture and engineering considerations.
Why it's worth reading:
While the OWASP Agentic Top 10 identifies major risks, this guide focuses on how organizations can address them throughout the application lifecycle.
It covers security considerations for agent memory, tool execution, API integrations, multi-agent coordination, and access to external systems.
Its lifecycle-oriented structure makes it particularly useful for engineering teams designing secure agent architectures and security professionals responsible for establishing technical requirements.
Multi-Agentic System Threat Modeling Guide
What it is:
Published in April 2025 by the OWASP Agentic Security Initiative, this guide introduces the MAESTRO threat modeling approach for multi-agent AI systems.
It examines security risks emerging when autonomous agents communicate, coordinate tasks, exchange information, and interact with shared infrastructure.
Why it's worth reading:
Traditional threat modeling methodologies do not always adequately capture the security implications of distributed autonomous decision-making.
MAESTRO provides a structured approach to identifying threats across interconnected agents, including trust boundary violations, coordination failures, compromised communications, and dependencies between agents.
The guide is particularly useful during architecture reviews and security design assessments, helping teams identify systemic risks before deploying complex multi-agent workflows.
Agent Name Service (ANS) for Secure AI Agent Discovery
What it is:
Published in May 2025, this OWASP GenAI Security Project publication proposes an architectural framework for discovering, identifying, and authenticating AI agents.
It explores how agent identity and discovery mechanisms could support secure communication and interoperability between autonomous systems.
Why it's worth reading:
As agents increasingly interact with other agents, organizations need mechanisms to establish which entities they are communicating with and whether those entities can be trusted.
ANS explores how verifiable agent identities, cryptographic assurance, and structured discovery could contribute to this trust infrastructure.
It is particularly relevant for security architects, IAM specialists, and organizations exploring agent-to-agent communication.
The framework remains conceptual, making it more useful for architectural planning and understanding emerging requirements than as a ready-to-deploy technical standard.
State of Agentic AI Security and Governance 2.01
What it is:
Updated in June 2026, this report examines the evolving security and governance landscape for autonomous AI systems. It brings together technical security considerations, governance frameworks, organizational approaches, and regulatory developments relevant to agentic AI adoption.
Why it's worth reading:
The report provides broader context for understanding why agentic AI requires security and governance approaches that extend beyond traditional model oversight.
Rather than concentrating on individual vulnerabilities, it explores how organizations can structure their approaches to developing, deploying, and managing autonomous systems.
It is particularly relevant for AI governance professionals, security leaders, and decision-makers who need to understand how technical agent security concerns connect with organizational accountability and regulatory expectations.
The report can support governance strategy development, internal discussions, and assessments of organizational readiness for agentic AI.
OWASP AI Maturity Assessment (AIMA) — Version 1.0
What it is:
A maturity assessment framework for evaluating how effectively organizations govern, secure, and manage AI systems. Building on OWASP's Software Assurance Maturity Model (SAMM), AIMA covers eight domains: Responsible AI, Governance, Data Management, Privacy, Design, Implementation, Verification, and Operations.
Why it's worth reading:
AIMA helps organizations assess not just whether security controls exist, but how consistently they are implemented, measured, and improved.
Its three maturity levels and structured assessment worksheets make it particularly useful for internal audits, governance assessments, and AI security improvement roadmaps. The framework also connects technical security practices with broader governance expectations under ISO/IEC 42001, NIST AI RMF, and the EU AI Act.
OWASP Artificial Intelligence Security Verification Standard (AISVS) 1.0
What it is:
Released on June 24, 2026, AISVS 1.0 establishes a structured catalogue of verifiable security requirements for AI-enabled systems.
Modeled after the OWASP Application Security Verification Standard, it covers security considerations throughout the AI lifecycle, from data collection and model development to deployment, monitoring, and retirement.
The framework defines three verification levels, ranging from baseline security requirements to advanced controls for high-assurance environments.
Why it's worth reading:
AISVS is particularly useful for organizations looking to move from risk identification toward testable security requirements.
Its structured approach enables security teams to define implementation expectations, establish assessment criteria, and evaluate AI applications against consistent requirements.
The verification levels also provide a way to scale security expectations according to system criticality and risk.
LLM and GenAI Security Center of Excellence Guide
What it is:
An organizational governance guide published by OWASP in October 2024. It explains how organizations can establish a Center of Excellence (COE) to coordinate secure and responsible generative AI adoption.
The guide proposes a multidisciplinary structure involving security, legal, data science, operations, and business stakeholders.
Why it's worth reading:
AI security challenges are rarely confined to a single organizational function. Effective governance requires coordination between technical teams, risk management, legal, and business leadership.
The guide provides an organizational blueprint for establishing responsibilities, developing security policies, coordinating assessments, and implementing operational safeguards.
It also includes example objectives, KPIs, implementation phases, and governance activities.
Particularly useful for organizations building their first formal AI security governance function or extending an existing AI Center of Excellence.
LLM AI Cybersecurity and Governance Checklist (Japanese Edition)
What it is:
A Japanese-language (But hey! what do we have LLM translation for?) OWASP checklist addressing the secure and responsible organizational adoption of LLM applications.
It brings together cybersecurity considerations, governance responsibilities, implementation questions, and references to established AI security resources, including OWASP and MITRE frameworks.
Why it's worth reading:
The checklist illustrates how AI security guidance can be translated into practical organizational adoption requirements.
Its coverage extends beyond technical vulnerabilities to considerations such as accountability, monitoring, transparency, privacy, fairness, and operational responsibility.
Although its language limits accessibility for some readers, it offers an additional perspective on integrating AI security considerations with broader governance and organizational readiness assessments.
Vendor Evaluation Criteria for AI Red Teaming Providers & Tooling v1.0
What it is:
Released in February 2026, this guide provides structured criteria for evaluating vendors offering AI red teaming services and testing platforms.
It addresses testing requirements across different AI architectures, including conversational applications, retrieval-augmented generation systems, tool-calling agents, MCP integrations, and multi-agent workflows.
Why it's worth reading:
The guide helps organizations distinguish comprehensive adversarial security assessments from narrowly scoped testing focused primarily on jailbreak attempts.
It identifies positive and negative indicators when assessing vendors, including threat-model relevance, testing rigor, tooling capabilities, and governance considerations.
Organizations can use the criteria when preparing procurement requirements, evaluating vendor proposals, or assessing the effectiveness of existing AI red teaming providers.
It is particularly relevant for security and procurement teams seeking to establish measurable expectations for external AI security testing services.
GenAI Incident Response Guide
What it is:
An 82-page guide published by the OWASP GenAI Security Project in July 2025. It addresses incident response challenges associated with generative AI systems and provides a framework for adapting organizational security operations to AI-specific threats.
Why it's worth reading:
Traditional cybersecurity incident response procedures may not fully address incidents involving model manipulation, prompt injection, unauthorized tool execution, or compromised AI-generated outputs.
The guide helps organizations consider how these scenarios should be identified, classified, investigated, escalated, and managed.
It also connects AI incident response with broader governance responsibilities, including documentation, accountability, and regulatory considerations.
This makes it particularly useful for security operations teams, incident responders, and AI governance professionals developing AI-specific incident management procedures.
The free section explain what can go wrong with AI systems. The Extra section focuses on how to assess, prioritize, and manage those risks in practice. Explore AI vulnerability scoring methodologies, crosswalks connecting OWASP risks with ISO, NIST, MITRE ATLAS, AIUC-1, and the EU AI Act, as well as agentic AI security controls and specialized technical guidance.
